
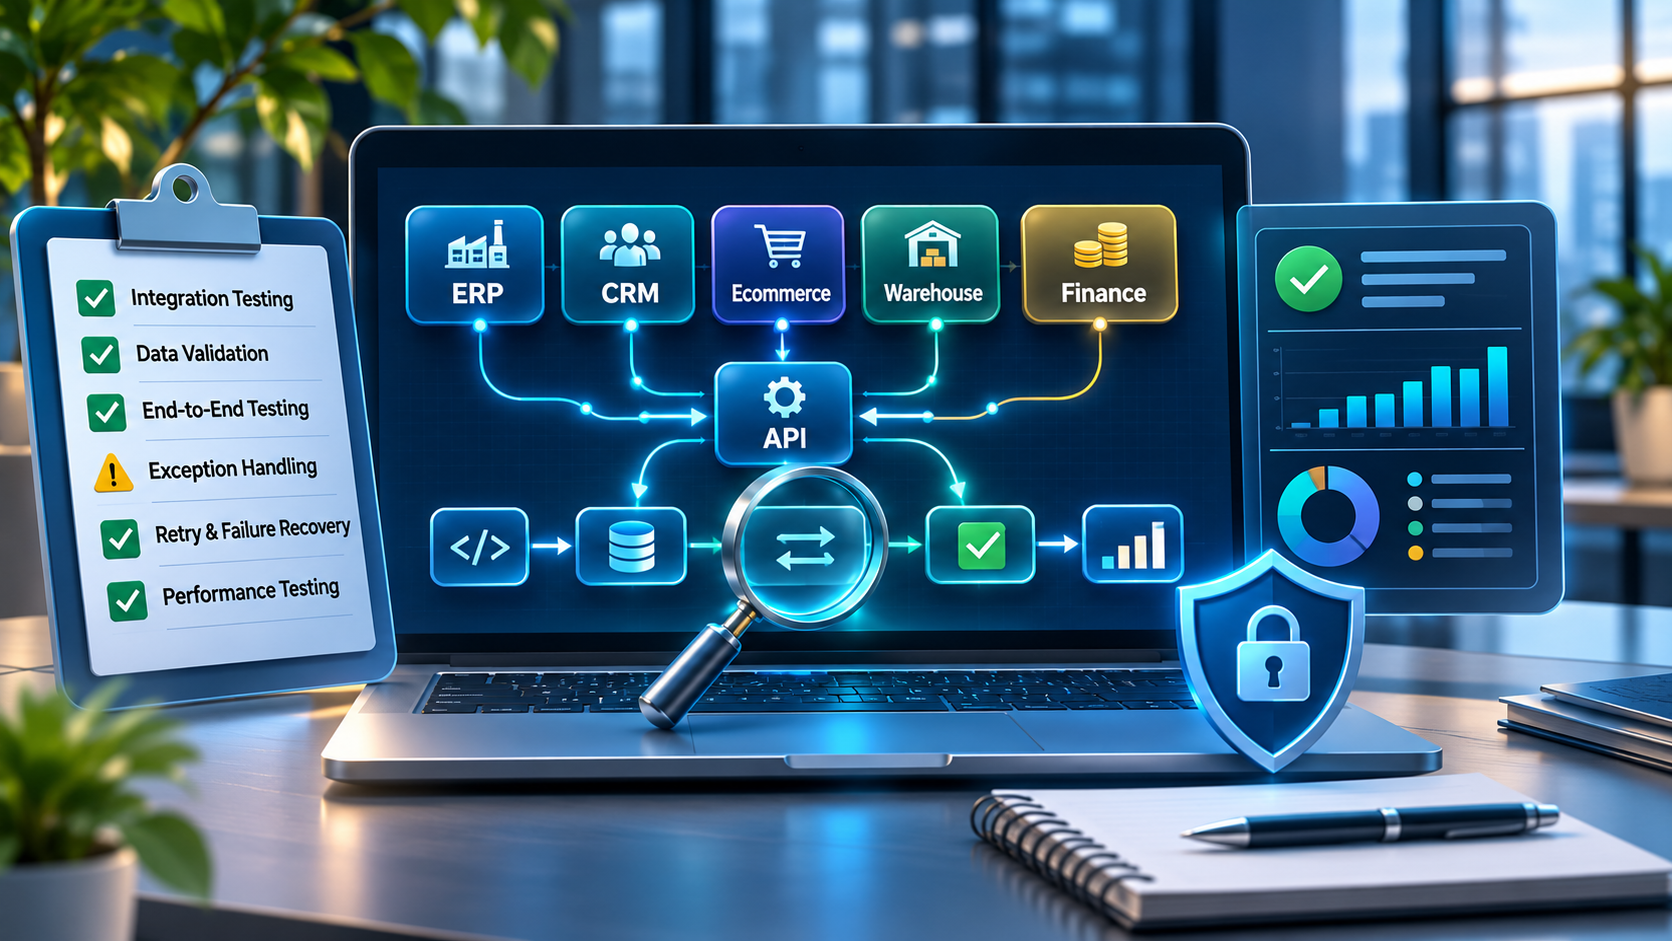
ERP integrations often pass a basic demonstration and still fail when exposed to real business volume, incomplete records, unusual transaction sequences or an unavailable downstream system. A successful API response does not prove that an order was created correctly, an inventory balance reconciled or a customer update reached every dependent application.
Integration testing verifies that systems, APIs, queues, data transformations and business processes work together as designed. This checklist is intended for ERP project managers, solution architects, QA leads, business process owners and implementation partners preparing for deployment or a major integration change.
What ERP integration testing must prove
- Data is transferred to the correct system and mapped to the correct fields.
- Business rules, units, currencies, dates and identifiers retain their intended meaning.
- Retries, duplicate messages, timeouts and partial failures do not create incorrect transactions.
- Security controls prevent unauthorised access and protect sensitive data.
- Critical processes complete across system boundaries, not just within individual applications.
- Failures are visible, recoverable and assigned to an accountable support team.
Map integrations to business processes
Begin with process flows rather than a list of endpoints. Identify the trigger, source system, receiving system, data contract, business outcome and reconciliation control for each interface.
| Business process | Example integration flow | Critical validation |
|---|---|---|
| Lead to customer | CRM prospect converted to approved ERP customer | Customer identity, legal details and duplicate prevention |
| Order to cash | CRM quote or ecommerce order sent to ERP | Price, tax, credit, quantity, order status and invoice linkage |
| Procure to pay | Supplier and purchase order shared with procurement or supplier portal | Supplier identity, approvals, currency and receipt matching |
| Inventory visibility | ERP stock availability published to ecommerce or CRM | Warehouse, unit, reservation, timing and available-to-promise rules |
| Finance reporting | ERP balances transferred to consolidation or analytics platform | Control totals, fiscal periods, dimensions and currency translation |
| Fulfilment | Warehouse shipment and delivery status returned to ERP or CRM | Partial shipment, cancellation, backorder and tracking references |
Build a layered test strategy
1. Unit and transformation tests
Test individual mapping functions, calculations, field conversions and validation rules. Include null values, maximum lengths, decimal precision, time zones, special characters and invalid enumerations. These tests are fast and should catch deterministic defects before systems are connected.
2. API and contract tests
Verify authentication, permissions, request and response schemas, required fields, version compatibility, status codes, throttling behaviour and error payloads. Contract tests help detect when a provider changes an API in a way that breaks a consumer.
3. Integration tests
Connect the relevant systems or representative test services and verify that data moves correctly through the real integration path. Test queues, transformations, database writes, event subscriptions and middleware configuration. Include both successful and failed exchanges.
4. End-to-end business process tests
Run realistic scenarios from the user’s starting action through the final business outcome. For example, create a sales order in CRM or ecommerce, validate it in ERP, fulfil it through warehouse operations and return shipment and invoice status. Business users should validate whether the process is usable and complete.
5. Non-functional tests
Assess throughput, latency, concurrency, resilience, security, monitoring and recovery. A flow that works for ten records may fail at month-end volume or when multiple legal entities process transactions simultaneously.
ERP integration testing checklist
| Test area | What to test | Evidence to retain |
|---|---|---|
| Connectivity | Authentication, endpoint availability, network and certificate configuration | Connection logs and access test results |
| Data mapping | Required fields, transformations, defaults, units, dates and currencies | Source-to-target comparison and mapping version |
| Identity and duplicates | Existing records, new records, alternate IDs and repeated requests | Cross-reference checks and duplicate report |
| Business validation | Credit limits, tax rules, price conditions, status transitions and approvals | Scenario results and business sign-off |
| Error handling | Invalid data, API errors, timeouts, rate limits and unavailable services | Error logs, retry history and exception ownership |
| Idempotency | Same request submitted more than once | Proof that duplicate side effects were prevented |
| Ordering | Out-of-order updates and dependent records arriving late | Sequence/version checks and recovery result |
| Reconciliation | Record counts, amounts, quantities and status totals | Signed control totals and variance explanations |
| Performance | Peak volume, concurrency, queue depth and processing latency | Load-test report and agreed thresholds |
| Security | Least privilege, secret handling, encryption and audit logging | Access matrix and security test evidence |
| Monitoring | Alerts, dashboards, dead-letter queues and support escalation | Operational runbook and alert test |
Test failure scenarios, not only the happy path
For each critical interface, deliberately test the conditions most likely to cause operational damage:
- The receiving API is unavailable after the source has committed the transaction.
- The request times out but the receiving system has actually processed it.
- The same message is delivered twice or replayed after recovery.
- A customer, product or supplier reference does not exist yet.
- A required parent record arrives after a child record.
- A field exceeds the target length or contains an unsupported value.
- A user or service account loses permission during processing.
- The source changes a record while an earlier update is still in flight.
- A downstream application is throttling requests or processing a backlog.
- A partial shipment, credit note, cancellation or order amendment changes the expected totals.
Define expected behaviour for each scenario: reject, hold, retry, route for manual review or compensate with a separate business transaction. Do not let the integration team invent recovery decisions during a production incident.
Reconciliation: prove that the business result is correct
Reconciliation should be designed into the integration, not added after a defect is found. Compare source and target record counts, unique identifiers, financial amounts, quantities, statuses and relevant date ranges. For financial interfaces, reconcile by company, currency, account and fiscal period. For inventory, reconcile by item, site, warehouse, location and unit of measure.
Set tolerances and define who approves variances. A zero-variance expectation may be appropriate for some financial totals, while asynchronous inventory updates may require an agreed latency window. Explain every accepted difference and retain the evidence used for sign-off.
Test environments and data management
Use environments that represent the integration topology closely enough to expose configuration and dependency problems. Lower environments can use controlled test services and smaller datasets, while pre-production should mirror critical production settings, security boundaries, network paths and realistic data volumes.
Use synthetic or masked data where possible. Protect personal, payment, payroll and commercially sensitive information. Refresh test data deliberately and document which system owns each test record. Avoid allowing test integrations to send real orders, invoices or customer communications to production endpoints.
Entry and exit criteria for go-live
Before testing begins, agree the requirements, scenario coverage, environment readiness, test data, defect severity model and business owners. Before go-live, require:
- All critical end-to-end scenarios passed in the release candidate environment.
- No open critical or high-severity defects without formally approved mitigation.
- Data reconciliation completed within agreed tolerances.
- Performance and security requirements met for expected workload.
- Retries, replay, alerting and recovery procedures demonstrated.
- Business process owners have signed off their scenarios.
- Support ownership, escalation paths and monitoring dashboards are operational.
- Cutover and rollback procedures have been rehearsed.
Common testing mistakes
- Testing APIs in isolation but not validating the full business process.
- Using only clean demonstration data and ignoring legacy data quality.
- Skipping duplicate, retry and out-of-order message scenarios.
- Assuming a successful HTTP response means the business transaction is complete.
- Leaving reconciliation until after go-live.
- Running only one end-to-end cycle at the end of the project.
- Failing to test service-account permissions and credential rotation.
- Not assigning owners to failed messages and unresolved data exceptions.
Final guidance
ERP integration testing is complete when the business can demonstrate reliable outcomes across connected systems, including when dependencies fail. Build tests from real business processes, validate data and security at every boundary, reconcile results and rehearse recovery. A repeatable evidence-based test cycle is more valuable than a large test-case count with no clear link to operational risk.
For wider project controls, see SeerOmega’s ERP implementation challenges guide and ERP data migration checklist.
Microsoft’s Dynamics 365 testing strategy describes testing across requirements, data, integration, security and end-to-end processes. The Azure Well-Architected testing guidance explains how to choose unit, integration and end-to-end test layers.
